Tiernan's Comms Closet

Geek, Programmer, Photographer, network egineer…

Building Cloud Images for Proxmox: 2026 Update

An update to my Proxmox cloud image post for 2026: Ubuntu 26.04, Debian 13 and AlmaLinux 10 (which needs an x86-64-v3 CPU type), a fix for clones sharing a machine ID, and a dhcpcd correction for Proxmox 9. Drafted by Claude, reviewed by me.

This post was drafted by Claude and reviewed by me. Claude checked the commands, the image links, and the libguestfs, systemd and Proxmox source code behind the machine ID fix; I checked it against my own setup.

Back in 2023 I wrote about building cloud images for Proxmox, and updated it in 2025 for Ubuntu 24.04. It’s time for another round: Ubuntu 26.04 is out, Proxmox 9 changed a few things, and I’ve finally worked out the machine ID problem from the bottom of the old post. This time I’ve added Debian 13 and AlmaLinux 10 too.

What’s changed since the old post

  • New images: Ubuntu 26.04 LTS (Resolute Raccoon), Debian 13 (Trixie) and AlmaLinux 10.
  • AlmaLinux 10 needs a newer CPU type. Like RHEL 10, it’s built for the x86-64-v3 level (AVX2). On Proxmox’s default CPU types it kernel-panics at boot, so the template needs --cpu x86-64-v3 or --cpu host. If your CPU has no AVX2 (some Pentiums and Celerons), Alma publishes an x86_64_v2 build as well.
  • Correction: install dhcpcd-base, not dhcpcd. The old note for Proxmox 9 said dhcpcd. The full package also runs a DHCP client service on the host, which grabs leases on bridges and guest firewall interfaces. One of my nodes ended up with three default routes because of it.
  • The machine ID problem is fixed in the image, with no need to boot each VM and patch it. The details are below, including why it happened.
  • Updated template commands: an explicit CPU type, import-from instead of qm importdisk, --boot order=scsi0 instead of the deprecated boot options, and DHCP set on the template.

On the Proxmox host

You need libguestfs-tools. On Proxmox 9 (Debian 13 underneath) you also need a DHCP client binary: virt-customize boots a small appliance to install packages, and without one it fails with dhcpcd: command not found and has no network.

apt update
apt install libguestfs-tools dhcpcd-base

If you followed my old note and installed dhcpcd, check ip route. If there’s more than one default route, fix it (with a console handy):

systemctl disable --now dhcpcd
apt remove dhcpcd        # keeps dhcpcd-base
ip route

Stopping it doesn’t remove the addresses and routes it added. Delete them with ip addr del, or reboot.

Pick a distro

Set these once; the rest of the commands are the same for all three.

Your storage name will be different. local-zfs is what my nodes use (the default on a ZFS install). Yours might be local-lvm or a name you picked: pvesm status on the host lists them, as does Datacenter → Storage in the web UI.

Ubuntu 26.04 LTS

VMID=9000
NAME=ubuntu-2604-cloudinit-template
IMG=resolute-server-cloudimg-amd64.img
wget https://cloud-images.ubuntu.com/resolute/current/$IMG

Debian 13

VMID=9001
NAME=debian-13-cloudinit-template
IMG=debian-13-genericcloud-amd64.qcow2
wget https://cloud.debian.org/images/cloud/trixie/latest/$IMG

AlmaLinux 10

VMID=9002
NAME=almalinux-10-cloudinit-template
IMG=AlmaLinux-10-GenericCloud-latest.x86_64.qcow2
wget https://repo.almalinux.org/almalinux/10/cloud/x86_64/images/$IMG

For the v2 build, replace x86_64 with x86_64_v2 in both the folder and the file name.

All three:

STORAGE=local-zfs                  # change to your storage
PROXY=http://10.244.71.183:3142    # change to your proxy's IP and port

Customise the image

I point apt at my apt-cacher-ng proxy and install the QEMU guest agent. If you run a proxy, set PROXY to your own proxy’s IP and port: 10.244.71.183 is mine and won’t exist on your network. If you don’t run one, drop the --append-line.

Ubuntu and Debian:

virt-customize -a $IMG \
  --install qemu-guest-agent \
  --append-line "/etc/apt/apt.conf.d/00proxy:Acquire::http { Proxy \"$PROXY\"; };"

AlmaLinux:

virt-customize -a $IMG \
  --install qemu-guest-agent \
  --selinux-relabel

--selinux-relabel matters on Alma: without it, files changed by virt-customize have no SELinux labels and services can fail to start. I skip the proxy here: Alma’s mirrors are HTTPS, and apt-cacher-ng only caches plain HTTP.

Sysprep and reset the machine ID

virt-sysprep -a $IMG
virt-customize -a $IMG \
  --truncate /etc/machine-id \
  --run-command 'rm -f /var/lib/dbus/machine-id && ln -s /etc/machine-id /var/lib/dbus/machine-id'
virt-cat -a $IMG /etc/machine-id | wc -c    # should print 0

Why clones were sharing an IP. systemd-networkd builds its DHCP client ID from /etc/machine-id. Two VMs with the same machine ID look like the same client to the DHCP server, so they get the same address, even with different MAC addresses.

When systemd boots and finds /etc/machine-id empty, it picks a new ID in this order:

  1. /var/lib/dbus/machine-id, if it’s a regular file with an ID in it.
  2. On KVM, the VM’s SMBIOS UUID.
  3. A random ID.

Proxmox gives every clone a new SMBIOS UUID, so a template with an empty machine ID produces a unique ID in every clone, on first boot.

virt-sysprep already empties both files. So if clones still share an ID, one of two things happened:

  • The template was booted before qm template. One boot is enough to write an ID, and every clone inherits it.
  • Something ran after virt-sysprep. Package installs can create a machine ID, so do sysprep and the reset last.

The virt-customize line above is my old manual fix, applied to the image instead of each VM. If you did boot the template, run cloud-init clean --logs --machine-id before shutting it down.

Create the template

qm create $VMID --name $NAME --ostype l26 --memory 4096 --cores 2 \
  --cpu x86-64-v2-AES --net0 virtio,bridge=vmbr0,tag=72
qm set $VMID --scsihw virtio-scsi-single \
  --scsi0 $STORAGE:0,import-from=$PWD/$IMG,discard=on,ssd=1,iothread=1
qm set $VMID --boot order=scsi0
qm disk resize $VMID scsi0 +50G
qm set $VMID --ide2 $STORAGE:cloudinit
qm set $VMID --serial0 socket --vga serial0
qm set $VMID --agent enabled=1
qm set $VMID --ipconfig0 ip=dhcp
qm template $VMID

For AlmaLinux 10, use --cpu x86-64-v3 (or host).

  • --cpu: without it, qm create uses kvm64, a Pentium 4-level CPU. x86-64-v2-AES works on any reasonably modern host and keeps live migration working. host is fastest, but migrating to a node with a different CPU can fail.
  • import-from: replaces qm importdisk plus qm set --scsi0. It needs an absolute path, hence $PWD.
  • virtio-scsi-single with iothread=1: gives each disk its own I/O thread. discard=on,ssd=1 passes TRIM through to thin storage.
  • VLAN 72 is my Kubernetes VLAN; remove ,tag=72 if you don’t need it.
  • Disk size: the cloud images are only 2-3 GB, so add space before templating.

Clone it

qm clone 9000 2001 --name k8s-01 --full
qm set 2001 --sshkey ~/godboxv3.pub --ciuser tiernano --memory 4096
qm start 2001

Change the IDs (9000 is the template, 2001 the new VM), the VM name (k8s-01), the username (tiernano), the SSH public key path (~/godboxv3.pub) and the memory to your own.

For a fixed IP, add --ipconfig0 to the qm set line, not to qm clone: qm clone only makes the copy, and the cloud-init settings (--ipconfig0, --sshkey, --ciuser) all belong to qm set. Set it before the first qm start. It replaces the template’s ip=dhcp for that VM only:

qm set 2001 --sshkey ~/godboxv3.pub --ciuser tiernano --memory 4096 \
  --ipconfig0 ip=10.244.72.21/24,gw=10.244.72.1

Use an address, prefix and gateway from your own network.

--full makes an independent copy. Without it you get a linked clone, which is quicker and smaller, but the template can’t be deleted while linked clones exist.

Check the machine ID on the clones

cat /etc/machine-id
journalctl -b | grep -i 'machine id'

Every clone should show a different ID, and the log should say Initializing machine ID from SMBIOS/DMI UUID. If two match, the template has an ID baked in: rebuild it from a fresh image.
Setting up Claude for my Dev Work

Ok, ok, before anyone says anything: yes, AI can be bad, but it can also be good. This post was not written by AI (it did review it, mostly for spelling and grammar). Some people think I don’t have any intelligence either… but that’s a different story.

Anyway, I’ve been using Claude Code and Desktop for a while to help with different personal projects, and I’ve added a few things to my setup to help with tasks. Here’s the list of what I use and what each one does.

  • jCodeMunch: Indexes your repo so the agent can pull just the function or class it needs instead of reading whole files. It helps organise large repos and makes it easier to find things in a project. Handy bit of kit. They claim it “cuts code-reading tokens by as much as 95% or more.” Free for non-commercial use; commercial use needs a one-time licence (from $79 for one developer). Haven’t purchased a licence yet, but plan to get it soon.
  • Context7: An MCP server that gives your AI agent up-to-date documentation for the libraries it’s working with. The free plan covers public libraries and 1,000 API calls a month; Pro ($10 per seat per month) adds private repos and gives 2,000 API calls. Pricing page has more details.
  • Headroom: Sits between your AI agent and the model endpoint and compresses tool outputs, logs and files locally before they’re sent. It’s available as a library, proxy or MCP server, and it’s open source (Apache 2.0). I’ve been running it for the last week or so and it has saved me about 5.6 million tokens so far. Heads up: it sends anonymous usage stats by default. Set HEADROOM_BEACON=off to disable them.
  • rtk: A single Rust binary that hooks into your agent and rewrites shell commands (for example, git status becomes rtk git status) so the model only sees compact output, reducing the data sent to the AI endpoint. Also open source (Apache 2.0). Note that it only filters Bash commands, not Claude Code’s built-in Read/Grep tools, and the “up to 90%” figure is a cut in command output, not your whole bill.

That’s what I’m currently using, but I’ll probably add more over time. If you’re using something I’ve missed, let me know.

Pricing and licence details as of September 2026.

New Video Series: Retro Corner

A few days back I started a new series on YouTube, named “Retro Corner”. The plan is to get some old hardware up and running (starting with the IBM ThinkPad R51e in video 1) and then continue on with some other machines (I have a couple of old Mac laptops coming in the next video) and networking (Dial Up, ISDN and, well… more on that soon…).

So, if you are interested, please subscribe and check out the videos. If there’s anything you’d like to see on the channel, please leave a comment.

Thanks.

Network Upgrades 2025

It’s been just over a year since I last posted my 2024 Network Upgrade post. In that time, my network has undergone several changes. Here are the major updates:

  • Swapped from a UDM Pro to a UCG Fiber.
  • Upgraded my FTTH link from 2Gb to 5Gb! (Hence the upgrade from the UDM Pro)
  • Added a UNAS Pro to the network for extra storage. It has 7x8TB drives in RAID 6, providing roughly 40TB of usable space (excluding the usual overhead).
  • Added an M4 Mac mini and an M1 Max Mac Studio to my M2 Mac mini and M1 Max MacBook Pro… That’s a lot of Macs!
  • Added Starlink to the mix of internet connections. Total bandwidth into the house is now around 6.5Gb/s, with upload at about 350Mb/s.

In the (hopefully not too distant) future, my cable ISP plans to upgrade from HFC (Hybrid Fiber/Coax) to full FTTH. When this happens, my speed will increase from 1Gb/50Mb to 5Gb/500Mb—and needless to say, I’ll be ordering that as soon as it’s available! This will boost the total download speed to just over 10Gb (about 10.4Gb, since Starlink tops out around 400Mb/s) and upload to 800Mb/s (with Starlink contributing 40–50Mb/s). That’s why I chose the UCG Fiber. It should handle two 5Gb incoming links, one 10Gb LAN connection, plus the Starlink connection (with IDS/IPS off, of course).

How to use Cloudflare Warp with a UDM Pro

If you’re considering using Cloudflare Warp for specific machines on your network, you can easily install the Warp client directly on them. It supports various operating systems, including Windows, Linux, Mac, iOS, and Android. However, if you need to use it on devices that aren’t compatible with the client installation (for example, NAS devices or smart TVs), this tutorial may be helpful.

First, please note that this is not an officially supported option. Cloudflare might modify their configurations at some point, potentially causing this feature to break. You have been informed about this possibility.

What you need:

  • UDM Pro (it can work on any Ubiquiti UniFi gateways, but this is the one I have).
  • WireGuard Configuration File Generator (WGCF). This tool will generate a WireGuard configuration file based on the Cloudflare settings.
  • I’ve created a script that executes the following commands. It worked on my MacBook Pro, and it should also work on Windows or Linux.

First, install WGCF. I installed it by running

brew install wgcf

on my MacBook Pro.

Next, run:

wgcf register

This will register a client on your machine. A wgcf-account.toml file will be left in your running folder. Next, run:

wgcf generate

You’ll be left with a wgcf-profile.conf file in your running folder. Open this file in a text editor to access the necessary details for your next steps.

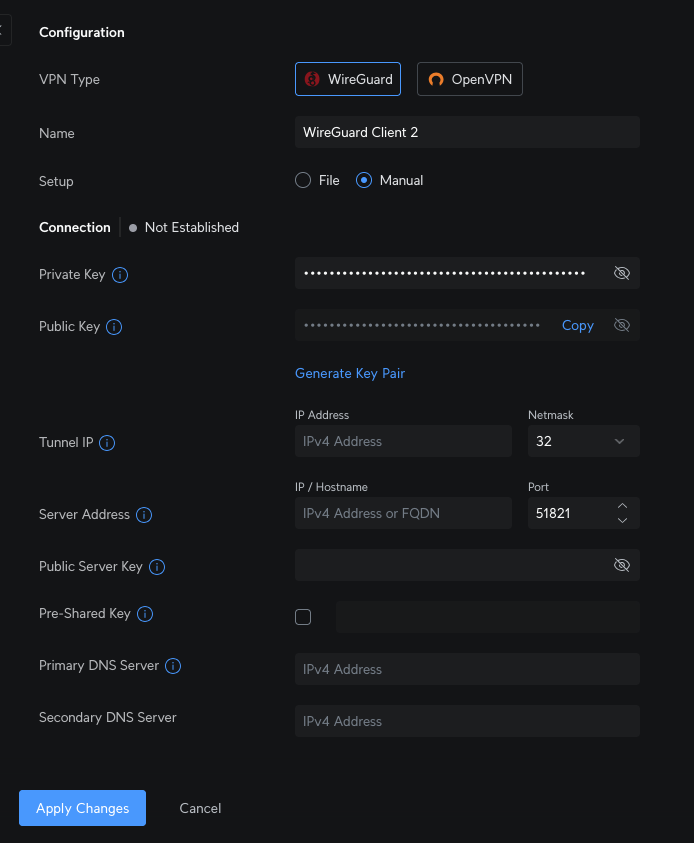
Go to your UniFi Network Dashboard, click on “Settings,” and then select “VPN” and “VPN Client.” Click on “Create New” and choose “WireGuard” as the protocol. Then, change the “Setup” to “Manual.”

The configuration file you created earlier should resemble this:

[Interface]
PrivateKey = <PRIVATEKEY>
Address = <IPv4Address>, <IPV6Address>
DNS = 1.1.1.1, 1.0.0.1, 2606:4700:4700::1111, 2606:4700:4700::1001
MTU = 1280
[Peer]
PublicKey = <ServerPublicKey>
AllowedIPs = 0.0.0.0/0, ::/0
Endpoint = <ServerEndpoint>

Use the contents of PrivateKey to overwrite the existing Private Key. This will automatically fill in your Public Key. Next, set your Tunnel IP to the value listed for IPv4Address. Remove the trailing slash and use that in the Netmask (my Netmask was a /32). Server Address is the value listed as ServerEndpoint. Check the port and include it as well. The Public Server Key is ServerPublicKey. Finally, add your DNS settings for IPv4 in the configuration and click Apply Changes.

After a few seconds, the status should change to “Connected”.

Next, you need to configure the Policy-Based Routes. This is located under the routing section, specifically under the heading “Policy-Based Routes.”

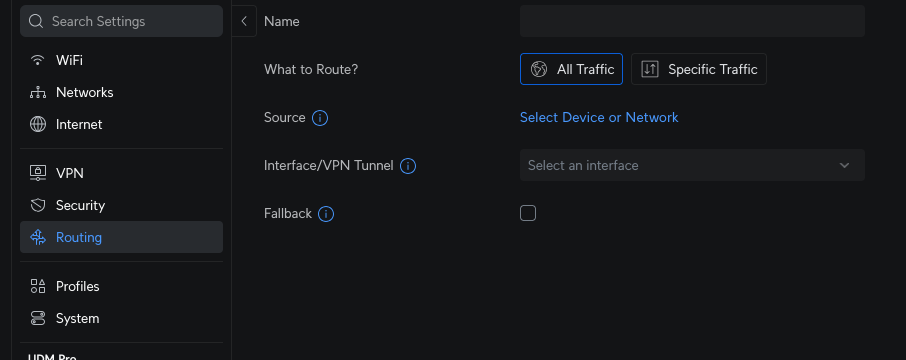
Here, you can name the rule and decide whether you want to send all traffic or specific traffic.

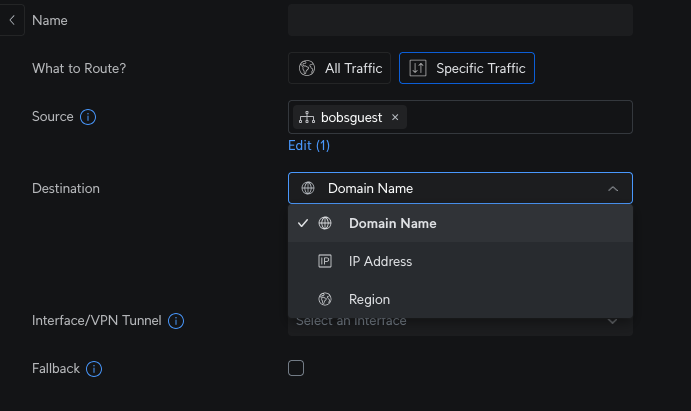
For all traffic, you can select a specific device or the entire network. For instance, in this example, all traffic from my Guest network will be routed through Warp:

You can also set it to send traffic to specific destinations:

Fallback allows it to fall back to one of the other connections if the Warp connection fails.

Finally, click Add Entry at the bottom. Now, run some tests on that machine and see the traffic counts increase.

That’s it. You can select what devices or networks, or even what destinations you want to send over Cloudflare. Happy hunting.

Step-by-Step Guide to Install Mac OS 9 in QEMU

Want to experience the classic Apple operating system on modern hardware? Emulating Mac OS 9 using QEMU is the way to go! This guide walks you through the process of setting up Mac OS 9 in QEMU, from creating a virtual hard drive to installing the operating system. Let’s get started!

Prerequisites

Before you begin, make sure you have:

  • A computer that can run QEMU (macOS, Linux, or Windows).
  • A Mac OS 9 installation ISO (like Mac OS 9.2.2 Universal Install. Check Archive.org).
  • A version of QEMU with sound support (like qemu-screamer).
  • You should also know a bit about using the terminal.

Step 1: Install QEMU

Download and install a version of QEMU that supports PowerPC emulation. The qemu-screamer fork is recommended for better audio support.

Clone the repository:

git clone -b screamer https://github.com/mcayland/qemu qemu-screamer

cd qemu-screamer

Configure and compile:

./configure --target-list="ppc-softmmu" --audio-drv-list="coreaudio" --enable-libusb --enable-kvm --enable-hvf --enable-cocoa

make

The compiled binary will be located in qemu-screamer/ppc-softmmu/qemu-system-ppc.

Step 2: Create a Virtual Hard Drive

Use the qemu-img tool to create a virtual hard drive for Mac OS 9:

./qemu-img create -f qcow2 macos9.img 2G

Replace 2G with your desired size if needed. Mac OS 9 does not require much space, so 2 GB is generally sufficient.

Step 3: Prepare the Installation Media

Ensure you have a bootable ISO of Mac OS 9. If you do not have one, download it from resources like “Mac OS 9 Lives” or Archive.org. Place the ISO in an accessible directory on your system.

Step 4: Start QEMU and Begin Installation

Run QEMU with the following command to boot into the Mac OS 9 installer:

./qemu-system-ppc \
-L pc-bios \
-cpu g4 \
-M mac99,via=pmu \
-m 512 \
-hda macos9.img \
-cdrom "Mac_OS_9.iso" \
-boot d \
-g 1024x768x32 \
-device usb-mouse \
-device usb-kbd

Explanation of key flags:

  • -cpu g4: Emulates a G4 processor.
  • -M mac99,via=pmu: Sets the machine type to emulate a PowerMac G4.
  • -m 512: Allocates 512 MB of RAM.
  • -hda macos9.img: Specifies the virtual hard drive.
  • -cdrom: Points to your Mac OS 9 installation ISO.
  • -boot d: Boots from the CD-ROM.

Step 5: Initialize and Install Mac OS 9

Once QEMU boots, open “Drive Setup” from the Utilities folder.

Select the uninitialized disk and click “Initialize.”

Choose “Mac OS Extended” as the file system and proceed.

After initializing, return to the installer and follow on-screen instructions to install Mac OS 9 onto your virtual hard drive.

The installation process typically takes about 7–10 minutes.

Step 6: Boot into Mac OS 9

After installation is complete:

Shut down QEMU.

Modify the boot command to boot from the hard drive instead of the CD-ROM:

    ./qemu-system-ppc \
    -L pc-bios \
    -cpu g4 \
    -M mac99,via=pmu \
    -m 512 \
    -hda macos9.img \
    -boot c \
    -g 1024x768x32 \
    -device usb-mouse \
    -device usb-kbd

Start QEMU again, and it should boot into your newly installed Mac OS 9 environment.

Optional: Enable Audio Support

If using qemu-screamer, audio can be enabled by ensuring CoreAudio is configured during compilation (–audio-drv-list=”coreaudio”). This setup allows sound output within Mac OS 9.

Tips and Troubleshooting

Backup Your Disk Image: After installation, back up your virtual hard drive (macos9.img) to avoid reinstalling if issues arise.

Adjust RAM: While Mac OS 9 can run on as little as 40 MB of RAM, allocating at least 512 MB ensures smoother performance.

Networking: Add networking support with flags like -netdev user,id=mynet and -device sungem,netdev=mynet.

By following these steps, you’ll have a fully functional emulation of Mac OS 9 running on QEMU! Enjoy exploring this nostalgic operating system.

VMware Workstation Pro and Fusion Pro now available for free for everyone

Back in May, VMware announced that VMware Workstation Pro and Fusion Pro would be free for non-commercial use. This was fantastic news for non-commercial users. However, a few days ago, they made an even better announcement: the free edition is now available to all users, including commercial users. While you can still purchase a license if you require support, the free version functions just as well, albeit without any support.


It appears that they are discontinuing Workstation Player and Fusion Player, as the functionality they offered is now included in the free version of Workstation and Fusion. 

How to Download Windows Server 2025 ARM edition (workaround)

In my previous post, I mentioned that Windows Server 2025 had gained general availability, but I had no information about the ARM64 version. It appears that 4sysops has found a workaround. You can download an ARM version of Windows Server 2025 from uupdump.net. Since I have a few M1/M2 Macs lying around, I’ll try downloading it and see if it works on them. I’m curious to know how long it would take someone to get this running on a Raspberry Pi. I believe they would make excellent little AD/DNS/DHCP servers. 

Windows Server 2025 GA’ed, along with System Center 2025

Microsoft has just released Windows Server 2025 and System Center 2025 in General Availability. You can find more information on the Microsoft Release status site.

Current status as of November 1, 2024 Windows Server 2025 is now generally available. It delivers security advancements and new hybrid cloud capabilities in a high performing, AI-capable platform. Windows Server 2025 is Microsoft’s latest Long-Term Servicing Channel (LTSC) release for Windows Server. To download a free 180-day evaluation, visit the Microsoft Evaluation Center. To learn more about Windows Server’s Lifecycle Policy, see the Windows Server 2025 lifecycle article. 


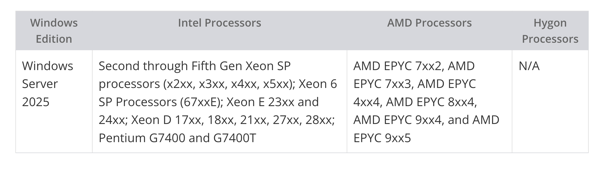
One aspect that hasn’t been discussed yet is the release of ARM64 support. While there were some ARM64 releases during the testing phase in the insiders group, there’s no official word on the GA versions yet. Additionally, here are the minimum requirements for CPUs (From Neowin).

The GodBoxV3, equipped with its first-generation Xeon SP processor, requires an upgrade to transition to Server 2025. Hmmm….

Building Cloud Images for Proxmox

To create an Ubuntu VM for a Kubernetes cluster using Proxmox, follow these steps: download and tweak the base image, sysprep it, create a template with specified configurations, and clone the VM. Adjust settings such as memory, storage, and IP configurations. Fix shared IP issues by resetting the machine ID.

[Updated] Updating this for 2025, including Noble as the image (24.04) and adding some other missing bits.

I needed to create a few Ubuntu VMs for a Kubernetes cluster for testing, and I wanted to make the process as simple as possible using Proxmox and some minimal automation. Here’s what I’ve done:

First, download the base image:

wget https://cloud-images.ubuntu.com/noble/current/noble-server-cloudimg-amd64.img

To be able to run the commands below, you need to install libguestfs-tools on Proxmox. An apt update and apt install libguestfs-tools is all that is needed.

Then, tweak the image. Since I’m using my apt-cacher-ng proxy here, I’ve set the proxy for all VMs. You can remove it or adjust it as needed. If you want to remove it, simply remove the append-line option. Additionally, I’m installing qemu-guest-agent here. You can add any additional items at this point if desired.

virt-customize -a noble-server-cloudimg-amd64.img --install qemu-guest-agent --append-line '/etc/apt/apt.conf.d/00proxy:Acquire::http { Proxy "http://10.244.71.182:3142"; };'

That command does the following:

– installs the QEMU Guest Agent
– adds the proxy script to apt config

NOTE: If you are running Proxmox 9, you will need to install dhcpcd first. So, apt update and apt install dhcpcd, then run the above commands.

Sysprepping the image resets it to the default state. If you don’t perform this step, and you clone the machine multiple times, all the clones will have the same machine ID and IP address. [Note: This isn’t working fully for me. See below for the changes I made to the machine ID.]

virt-sysprep -a noble-server-cloudimg-amd64.img

Create the template. I used ID 9000 and assigned a name. You can modify this. Additionally, I’ve tagged mine with VLAN 72 (my Kubernetes VLAN). Feel free to change or remove this tag as needed. Furthermore, I set the disk size to add 50GB. Please replace any references to “godboxv2-tank” with your storage name.

qm create 9000 --name "ubuntu-2404-cloudinit-template" --memory 4096 --cores 2 --net0 virtio,bridge=vmbr0,tag=72
qm importdisk 9000 noble-server-cloudimg-amd64.img godboxv2-tank
qm set 9000 --scsihw virtio-scsi-pci --scsi0 godboxv2-tank:vm-9000-disk-0
qm set 9000 --boot c --bootdisk scsi0
qm disk resize 9000 scsi0 +50G
qm set 9000 --ide2 godboxv2-tank:cloudinit
qm set 9000 --serial0 socket --vga serial0
qm set 9000 --agent enabled=1
qm template 9000

This does the following:

– creates a new VM with id 9000 and sets the name, memory and core count. It also sets the network card, and in my case the VLAN (remove ,tag=72 if you do not need a VLAN)
– imports the disk to the VM and puts it in the storage path. You will need to change your path here.
– sets the VM to use that disk as a SCSI drive
– sets the disk to be bootable
– sets the size of the disk to +50GB of what it was originally… important as the disk is only a couple of GB and you will run out of space quite quickly…
– sets up cloud init for the VM as an IDE CD drive.
– sets serial output for the VM
– tells Proxmox the Agent is installed
– sets the VM as a template.

Next, clone the template into a new VM.

qm clone 9000 2001 --name k8s-01
qm set 2001 --sshkey godboxv3.pub
qm set 2001 --memory 4096
qm set 2001 --ciuser tiernano
qm set 2001 --ipconfig0 ip=dhcp

Here we are creating a new VM with ID 2001, setting the SSH key, setting the memory and user, and telling the machine to get its IP from DHCP. 

Change tiernano and godboxv3.pub to your settings. Modify the names and memory as necessary.

As mentioned earlier, I’m still encountering the issue of IP addresses being shared. To resolve this, log into the boxes and execute the following commands:

echo -n > /etc/machine-id
rm /var/lib/dbus/machine-id
ln -s /etc/machine-id /var/lib/dbus/machine-id

Reboot the VM, and the problem should be resolved.